Skip to content
SVENNISAIWe speak Claude.
Blog · Claude Team

Claude Team admin settings for the owner: what to set up first

A practical guide to the Claude Team admin settings an owner should configure first, from the Owner role and seat types to connectors, data retention and spending caps.

10 min read

Book a 30-minute call · with a Claude Certified Architect from our team.

Article · 10 min read
Abstract layered panels with small switches settling into an ordered row, suggesting workspace settings being configured

Claude Team admin settings for the owner: what to set first

Claude Team admin settings for the owner come down to four jobs, done in this order. Decide who holds the Owner role, and invite members on the right seat type. Set the rules for data and connectors, then set billing and spending limits. Finish those before the team starts work and most later clean-up never happens.

Claude Team admin settings are the organisation-wide controls an Owner uses to manage members, seats, sign-in, connectors, data and billing for everyone on the plan. Claude Team is Anthropic's plan for teams of 2 to 150 people, according to the Claude pricing page. In this guide, the Owner means the account that controls those organisation-wide settings, including which connectors the organisation enables.

This guide covers the owner's side only, not how to prompt Claude. Where published sources disagree about what Team includes, the guide says so. In those cases, confirm the point in your own admin settings.
The Owner role comes first, because the Owner controls what Claude reaches

The Owner role should go to someone who will still be accountable for Claude in a year, not to whoever signed up first. The Owner controls the organisation-wide settings, including which connectors the organisation enables. On Enterprise, dope.security reports that an Owner must enable a connector before anyone can use it. That makes the Owner the gatekeeper for what Claude can reach.

Role-based permissions are where Team and Enterprise differ. TrueFoundry's governance guide and dope.security both describe fine-grained role-based access as something Enterprise adds on top of Team. Expect a simpler role set on Team, and check which roles your console offers before you assign them.

Three decisions about the Owner role belong at the very start:

  • Who holds the Owner role day to day.
  • Who covers when that person is away or leaves the company.
  • Whether managers need admin rights, or only a seat.

Keep admin rights to as few people as possible. Every extra admin widens the group that can change settings for the whole organisation.

Members and seat types: standard seats for most, premium for heavy users

On Claude Team, members join by manual invite. Automated provisioning through SCIM is an Enterprise feature, as AI Codex's comparison of Team and Enterprise for IT sets out. SCIM is a standard that creates and removes user accounts automatically from your company directory. On Team, someone must remove leavers by hand, so add that step to your offboarding list.

Each Claude Team member gets one of two seat types. A standard seat includes Claude Code, Anthropic's coding tool, according to the Claude release notes. A premium seat gives five times the usage of a standard seat, per the pricing page.

The pricing page adds that Claude Code shares the same usage limits as the rest of the plan. A member who codes heavily will therefore reach limits sooner than one who only chats.

Start almost everyone on a standard seat. Move a person to premium only when their own usage shows they hit limits often. Ask which tasks hit the limit before you upgrade. Sometimes the fix is a better-structured project rather than more usage.

Sign-in options by plan: SSO on Team, SAML and SCIM on Enterprise

Single sign-on, or SSO, lets staff sign in to Claude with their existing company account instead of a separate password. dope.security's overview of Claude controls says SSO and domain verification come with both Team and Enterprise. AI Codex adds a limit: Team SSO works through Google or Microsoft only, while Enterprise supports SAML with any identity provider.

An identity provider is the system that holds your staff accounts, such as Okta or Azure AD. TrueFoundry describes the SAML route in three steps. You verify domain ownership with a DNS TXT record and upload the identity provider's metadata to the Claude Admin Console. Then you connect a SAML 2.0 provider. If your staff already sign in with Google or Microsoft accounts, the Team route matches what you have.

Domain capture is the claiming of your verified email domain, so that Claude accounts using it belong to your organisation. dope.security describes it as an Enterprise feature. Anthropic calls the process one-way, with a 30-day migration window. Check your own console before you rely on it on Team.

One limit holds on any plan. Domain capture does not reach accounts created with personal addresses such as Gmail. It is not a control for personal accounts used on company devices.

Data retention, memory and model training on Claude Team

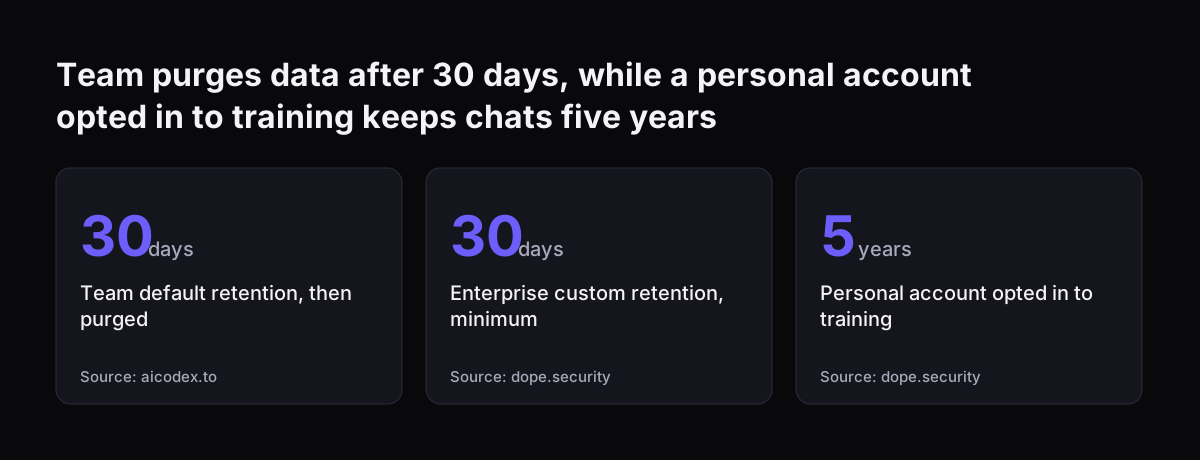
Claude Team keeps data for 30 days by default and then purges it, according to AI Codex. Enterprise lets admins set custom retention, with a 30-day minimum, per dope.security. On Team you work with the default. If you need a different retention period for audit reasons, that is an Enterprise question.

Memory is off by default for Team and Enterprise organisations, the release notes say. On Free, Pro and Max it is on by default. Turning memory on for a Team workspace is therefore an Owner decision, not a default you inherit. Leave it off at launch and decide once the team has settled in.

Model training is the strongest reason to move staff off personal accounts. Anthropic states that Team and Enterprise content is not used for model training by default, dope.security reports. On Free, Pro and Max, users choose whether their chats train models. Opting in means five-year retention, per dope.security.

Logging also differs by plan. Audit logs and the Compliance API are Enterprise features. The Compliance API lets an organisation query user activity, conversations and admin changes programmatically. Enterprise audit log exports cover the past 180 days. On Team, plan your oversight knowing these tools are not there.

Team purges data after 30 days, while a personal account opted in to training keeps chats five years: Team default retention, then purged 30 days, Enterprise custom retention, minimum 30 days, Personal account opted in to training 5 years
Source: aicodex.to, dope.security

Connectors and data access: who may install them and what they reach

A connector is the link that lets Claude read from, and sometimes act in, another program. Write access is the connector decision that matters most.

With write tools enabled, the Microsoft 365 connector lets Claude draft, send and organise email, and manage calendar events. It can also create and update files in OneDrive and SharePoint, per the release notes, while Teams stays read-only. Our post on connecting Claude in Microsoft 365 and Teams walks through that connector.

Enterprise offers tighter connector control. There, an Owner must enable a connector before anyone can use it, dope.security reports. The Owner can set each tool to always allow, needs approval or blocked. Enterprise also adds managed policies for MCP and tool permissions that users cannot toggle around. On Team, the Owner's organisation-level choices are your main control point.

Your own business systems, such as Zoho CRM, need a custom connector or an MCP server. An MCP server is a program that sits in front of a system and offers its data and actions to Claude. At Svennis, we write down every connection before anyone enables it: who will use it, and whether Claude may write to it. We then show the client each option with its cost, a connector, an MCP server, a plugin or a skill, and the client picks one.

The plugins directory guide for a small team covers which ready-made plugins to consider before you build anything.

Billing, usage limits and spending caps on Claude Team

Claude Team standard seats cost $20 per seat per month billed annually, or $25 billed monthly, on the Claude pricing page. Premium seats cost $100 per seat per month billed annually, or $125 billed monthly. Check the figure shown when you sign up.

Usage limits reset on a rolling five-hour window, and paid plans add weekly limits on top. Usage credits are the option to keep working at standard API rates after someone reaches a limit. Turning them on keeps work moving. It also turns a fixed monthly bill into a variable one.

Spending caps need checking in your own console. AI Codex says Team bills per workspace and that per-user caps require Enterprise. If you need a cap per person, confirm your console offers one before you rely on it.

The pricing page also lists up to $500 per month in pooled API credits on Team. These credits are for running your own apps and agents on the Claude Platform, the release notes say. Our guide to what Claude costs and how to start puts these numbers into a yearly budget.

Claude Code on Team seats: managed settings for anyone who codes

Claude Code needs its own policy because it does more than chat. TrueFoundry describes it running in the terminal with full user-level privileges. It reads files, runs bash commands, connects to MCP servers and sends code context to Anthropic's servers for processing. Every Team standard seat includes it, so decide early who should use it.

Team plans support managed settings for Claude Code; Free, Pro and Max have none. The tool is managed-settings.json, a file that enforces organisation-wide Claude Code policies developers cannot override. Your device management software pushes it to a fixed path on each machine:

  • macOS: /Library/Application Support/ClaudeCode/managed-settings.json
  • Linux: /etc/claude-code/managed-settings.json

Two Claude Code settings deserve attention first. With allowManagedMcpServersOnly set to true, only MCP servers defined in managed settings can run. Without disableBypassPermissionsMode, a developer can run Claude Code with --dangerously-skip-permissions and bypass every safety check you set.

TrueFoundry also notes that server-managed settings, still in beta, are client-side only. A user with sudo access can tamper with them. The desktop side is covered in our post on installing Claude desktop and its admin settings.

Worked example: a twelve-person firm's first admin session on Claude Team

Take a hypothetical twelve-person accountancy firm moving onto Claude Team. Staff sign in with Microsoft accounts. Two people already use personal Claude accounts, and one partner does heavy analysis every day. The Owner works through the admin settings in one sitting, in this order:

  1. Owner role. The managing partner takes the Owner role, and the office manager is named as cover.
  2. Seats. Eleven standard seats and one premium seat for the analyst partner. At annual billing that is $220 plus $100, so $320 a month before tax.
  3. Sign-in. Microsoft SSO, if the console offers it. The two personal-account users get Team invites and stop using personal accounts for client work.
  4. Memory. Left off for the first month.
  5. Connectors. Microsoft 365 enabled at organisation level, without write tools. Write access waits until the firm has a written rule on what Claude may send.
  6. Billing. Annual billing, an organisation-wide spending cap, and usage credits off until the first month's usage is known.
  7. Claude Code. Nobody in the firm codes, so the Owner notes it as a later decision.

The firm ends the session with a known monthly cost and one connector live. Every later change becomes a deliberate decision rather than an inherited default.

Claude Team admin checklist: the settings in the order to set them

This checklist puts the owner's Claude Team settings in order. For each one it shows what Team offers, according to the sources above, and a sensible first choice. Where sources disagree, the middle column says so.

SettingOn Claude TeamFirst choice
Owner roleOwner controls organisation-wide settings, including connectorsOne named Owner plus named cover
MembersManual invites; SCIM is Enterprise onlyAdd removal of leavers to offboarding
Seat typeStandard, or premium with five times the usageStandard for all; premium on evidence
Sign-inSSO through Google or Microsoft; SAML with any provider is EnterpriseMatch your existing staff accounts
Retention30 days by default; custom retention is EnterpriseAccept the default, or move to Enterprise
MemoryOff by defaultLeave off at launch
ConnectorsRead or write access, such as Microsoft 365 write toolsRead access first; write tools later
Usage creditsKeep working at API rates after a limitOff until you know normal usage
Spending capsPer-workspace billing; per-user caps are Enterprise, per AI CodexConfirm what your console offers
Claude CodeIncluded on standard seats; managed settings supportedPush managed settings before developers start

Review the checklist after the first month. Real usage then shows which seats, connectors and limits the team actually needs.

What Claude Team admin settings mean for a UK company

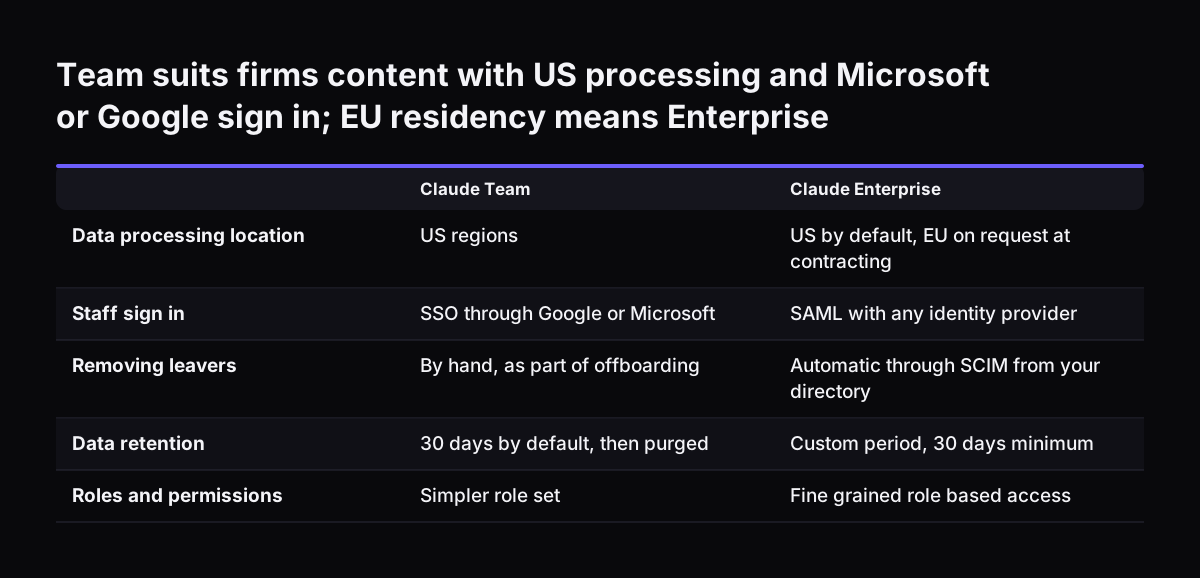
Data location is the first point for a UK company on Claude Team. Team processes data in US regions, AI Codex reports. Enterprise is US by default, with EU and other residency options available on request during contracting. If your data protection review requires processing outside the US, that points to Enterprise rather than to any Team setting.

Prices on the Claude pricing page are in US dollars. Budget from the price shown when you sign up, not from a figure in an article.

Personal accounts are the common gap in UK firms. Domain capture does not reach accounts created with personal addresses such as Gmail. Staff who opted into training on a consumer plan have five-year retention on those chats. Moving that work into the Team workspace, where Anthropic says content is not used for training by default, is the practical fix.

Enterprise is now easier to buy for a mid-sized firm. Any organisation can purchase it directly on the website without a Sales conversation, the release notes say. The pricing page lists it at $20 per seat per month plus usage at API rates, billed annually, with a 20-seat minimum.

Team suits firms content with US processing and Microsoft or Google sign in; EU residency means Enterprise. Claude Team / Claude Enterprise. Data processing location: US regions / US by default, EU on request at contracting; Staff sign in: SSO throug

Next steps for the owner of a new Claude Team workspace

Your next step is one admin session with the checklist above, ideally before most staff receive invites. Name the Owner and cover, and choose seat types. Set sign-in, leave memory off, enable one connector and set a spending cap. Then let the team work for a month before you change anything.

For shared work after setup, our guide to setting up Claude Projects and skills for a small team covers what to build first. Write down any rule you set, such as when Claude may send email, so new members inherit it.

If you want a partner alongside you, Svennis works in four steps: the Workshop, a pilot, the department Activation, then monthly operations. Pilot Claude B puts Claude Team in place for the whole team, including the admin settings in this guide. Pilot Claude A instead builds an AI agent on Claude for one process.

Sources

  1. Claude Help Center: Release notes
  2. Anthropic: Plans and pricing
  3. TrueFoundry: Claude Code governance
  4. dope.security: Claude Enterprise controls
  5. AI Codex: Claude Team vs Enterprise for IT and legal
Free, 30 minutes

Pick a time. Bring the process this article made you think of.

You leave with a clear yes or no on putting Claude on it, and the step that fits from our published prices. You speak to someone who builds the agents, not a salesperson.

Prefer to call? +44 7588 772736 · Not ready to talk? See it on your business first.

30 minutes · video call · free
  1. 1Time
  2. 2Details
  3. 3Booked